Secured Socket Layer (SSL) is the cryptographic protocol that is used to establish secured internet communication. Regular internet users always come across several websites. Some websites initiate with “HTTP” however some of them initiate with “HTTPS” in their domain name. The extra “S” in “HTTPS” means “secure”. Domain name with “HTPPS” in websites indicates that all the data provided to this website will be private between the website and the user, and it will be protected from the third-party.
What is an SSL certificate?
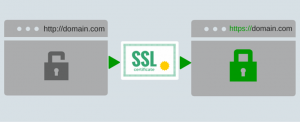
SSL certificates are small data files hosted on the origin server of the website. SSL certificates enable the SSL/TLS encryption and contain the website’s identity as well as the public key. With SSL an encrypted link can be established between the web server and browser. It is mostly used for e-commerce website and pages that request to users for their valuable information. But, nowadays almost all websites need to protect the data of their website visitors with SSL certificate.
Importance of SSL Certificate
The main reason to use SSL is to establish a secure path to transmit sensitive information over the internet.
Sensitive data protection
With the advent of the Internet, cybersecurity professionals have made strenuous efforts to secure websites. However, hackers are also creative. They always use new techniques and technologies to break security. The security of your data on the Internet is very important. When you share any data with a website, it goes through many computers to reach the destination computer. If any of these devices are hacker and once they find it insecure, they steal all your valuable information.The SSL certificate provides a cryptographic encrypted link that encrypts each of your information. Client-server communication is protected if an SSL certificate is used for the website. Using SSL will guarantee the protection of sensitive data such as login credentials, credit card information and other personal details.
Read about Ways to improve website security and prevent hacking
More visibility and more traffic
Google examines various components of a website in order to rank it. Google Webmaster Trends analysts say SSL certification is a key component of their ranking algorithms. A secure website with HTTPS is required to get high position on Google. The higher the rank of the website means the more likely you are to click the link. That way, you can get more website traffic to your website. Increased website traffic increases leads and sales potential. The higher rank from Google adds more value to the brand reputation.
Improves customer trust
SSL certificates are extremely important from a customer perspective. Normally no one will stop at a website that warns you are not safe. Customers will also switch to another website if the previous website warns them that the website is not secure. Having "HTTPS" with the website ensures that customers' sensitive data is protected. This security assurance of user data helps increase customer confidence. This is the best way to attract repeat business.
Enables secured payment transaction
Details of online payment transactions are always targeted by hackers to steal customers' hard earned money. Hackers are always looking for vulnerabilities to attack. SSL establishes an encrypted connection to protect all the details of online payment transactions. This is another great reason to get a trusted customer. SSL should not be considered limited to e-commerce websites because cybercriminals seek out any personal information of customers to target them and fulfill their evil intentions.
Types of SSL certificate
-
Domain validated (DV):
These SSL certificates come with the lowest reliable level of security. CA sends a confirmation email to the website's registered email address to verify identity. It does not require any additional information for business verification. It is often used by cyber criminals because it is easier to get a website and it appears more secure than it really is.
-
Organizationally validated (OV):
To obtain OV certificates, the CA verifies a number of business details, such as the organization, its location, and the domain name of the website. The OV certification process requires a period of a few days. These certifications have a moderate level of reliability so this is a great option for a website that deals with less sensitive data transactions.
-
Extended validation (EV):
These certificates are ideal for websites that transfer sensitive data over the network. It has come up with a high level of security trust. CA verifies the more detailed information of the business to issue the certificate. This process includes verification of the applicant's identity, corporate documents and third-party database information verification. Users can identify EV certified websites by checking the padlock and company name in green.
How does SSL certificate works?
SSL certificates primarily use public-key cryptography. This particular type of cryptography takes advantage of the power of two keys that are long strings of random numbers. One is a private key and the other is a public key. The server knows a public key that is available in the public domain. Encrypting any message is helpful. Consider the example, if A is sending a message to B, then A encrypts message with public key and sends to B. If B receives message, he decrypts it with the private key he has. When the public key is publicly available, the private key is kept private only to the authorized recipient who uses it to decrypt the message. If any other third-party device comes through this transition, it can only get lines of encrypted code that are impossible to crack without a private key.
From where should we buy an SSL certificate?
The SSL certificate should be issued by the Trusted Certificate Authority (CA). Mobile devices, operating systems and browsers keep a list of trusted CA root certificates. The root certificate must be on the end user's machine to trust the certificate. If the certificate is not trusted, the browser displays an untrusted error message to the end user. Untrusted certificate reduce customers trust in the website and thus lose customers.
Result of expired SSL certificate
Like other services, the SSL certificate has an expiration date, the expiration of which may expose the website to serious risks.
- Insecure website negatively affects customer trust.
- Risk of losing loyal customers.
- Negative impact on business reputation and brand.
- Increased insecurity of customer sensitive data.